What Is Pharming and How Do You Prevent It?


Introduction
Pharming blends "farming" and "phishing" into a single word for a specific kind of scam: tricking you into landing on a fake website by manipulating the plumbing that routes your traffic there, rather than by tricking you into clicking a malicious link.
What Is Pharming?
Pharming is the malicious redirection of a website or app to a fake version of itself, designed to harvest login credentials or other sensitive data. Unlike phishing, which relies on a lure (a convincing email, a fake text), pharming can redirect you even if you type the correct address yourself or use a saved bookmark. The redirection happens after your device sends its connection request, which is exactly what makes it so dangerous: the usual advice of "check the link before you click" does not help if the manipulation happens at the network or device level, not the link itself.
Is your cellphone vulnerable to SIM Swap? Get a FREE scan now!
Please ensure your number is in the correct format.
Valid for US numbers only!
How Does a Pharming Attack Work?
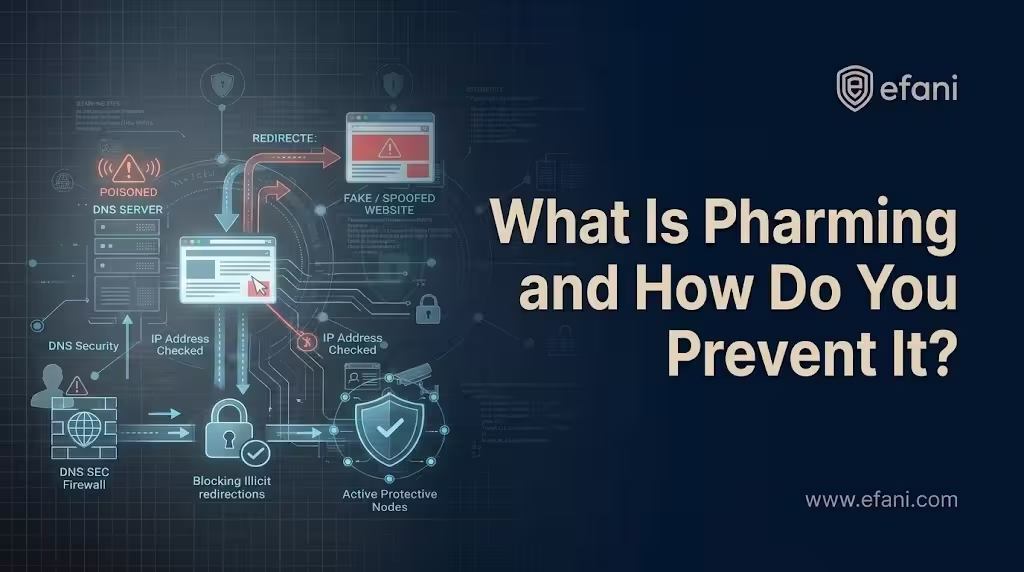
Pharming tampers with the systems that translate a readable address like www.yourbank.com into the numeric IP address your browser actually connects to. That typically happens one of two ways:
- Malware-based pharming. A Trojan or virus, often delivered through a malicious email attachment or link, gets installed on a victim's device and modifies the local "hosts" file, the file your computer checks before even asking the internet how to reach a given address. Once that file is altered, typing the correct address no longer matters. The infected device sends you to the fraudulent site every time.
- DNS poisoning (DNS cache poisoning). Rather than infecting one device, the attacker corrupts entries in a DNS server itself, the shared directory that translates domain names to IP addresses for many users at once. A single poisoned DNS server, especially one further up the chain like an ISP's, can silently redirect a large number of victims to a fake site, which is why DNS poisoning is considered the more dangerous and scalable of the two techniques.
Pharming vs. Phishing: What's the Difference?
Phishing relies on a lure: a fake email, text, or message designed to get you to click something. Pharming needs no lure at all. Once the malicious code or DNS entry is in place, you are redirected automatically, with no social-engineering step required on your part at that moment. That is why pharming is sometimes described as "phishing without the hook." It is also, generally, less common than phishing in absolute terms, simply because it takes more technical effort for the attacker to set up.
Notable Pharming Incidents
Pharming is not a theoretical risk. Three documented cases show how differently it can play out:
A 2007 attack on more than 50 financial institutions. Security researchers at Websense uncovered a pharming Trojan that silently installed itself on victims' machines by exploiting an unpatched Internet Explorer vulnerability (MS06-014). Once installed, the malware rewrote parts of the login pages for more than 50 banking and e-commerce sites across the US, Europe, and the Asia-Pacific region, so that credentials typed into what looked like a normal login page were sent straight to a server in Russia. At its peak, the campaign was linked to over 1,000 successful infections a day before the hosting sites, based in Germany, Estonia, and the UK, were shut down. (The Register, February 2007)
A 2015 router-hijacking campaign in Brazil. Proofpoint identified a campaign that sent roughly 100 phishing emails, mostly to Brazilian users, containing a link that exploited a cross-site request forgery flaw in UTStarcom and TR-Link home routers. If the exploit worked, the attacker reached the router's admin console, tried the device's default login credentials, and, if those worked too, changed its DNS settings, redirecting every device on that home network to the attacker's own servers. (CSO Online, February 2015)
A 2019 DNS-manipulation attack tied to Venezuela's humanitarian aid drive. Days after Venezuelan opposition leader Juan Guaidó launched a real "Voluntarios por Venezuela" volunteer sign-up site, a near-identical fake domain appeared. Inside Venezuela, both the real and fake domains resolved to the same IP address, the one controlled by the fake site, so volunteers entering their name, national ID number, phone number, and address could end up handing that information to the fake site no matter which domain they actually typed. (Kaspersky Securelist, February 2019)
Taken together, these three cases span the full range of how pharming is actually carried out: a server-side credential-harvesting Trojan, a consumer-router DNS hijack, and a DNS-level manipulation aimed at a specific population.
SIM Swap Protection
Get our SAFE plan for guaranteed SIM swap protection.
Signs You May Be a Pharming Victim
- Financial activity you did not initiate
- Email replies to messages you never sent
- Unfamiliar posts or activity on your social accounts
- Security software (antivirus, anti-malware) that has been disabled without your action
- New software or browser extensions you did not install
- Frequent, unexplained pop-ups or redirects to unfamiliar sites
- A device that suddenly runs slower, hangs, or crashes more than usual
Monthly
Yearly
How to Protect Yourself From Pharming
- Keep your router firmware updated and change its default admin password. Router-based pharming almost always starts with default or weak credentials.
- Use a reputable, security-conscious ISP and, where available, a DNS resolver that supports DNSSEC and filters known-malicious domains.
- Check for HTTPS, every time, not just the first time you visit a site. A missing or broken HTTPS certificate on a site you normally trust is a red flag.
- Look closely at the URL itself. Pharming and look-alike domain attacks often rely on changes subtle enough to miss at a glance.
- Enable two-factor authentication everywhere it's offered, so a stolen password alone is not enough to compromise your account even if you are briefly redirected to a fake login page.
- Run updated antivirus/anti-malware software and scan regularly, since malware-based pharming depends on an initial infection you may not otherwise notice.
As a summary of the core defense priorities:
- Secure the router (firmware + credentials)
- Secure the DNS path (trusted ISP/resolver, DNSSEC where available)
- Secure the login (HTTPS checks + MFA)
- Secure the device (updated anti-malware)
Why Mobile Account Security Belongs in This Conversation
Pharming is dangerous because it bypasses your usual vigilance about links and emails. SIM swapping is the mobile equivalent: it bypasses your password entirely by hijacking the phone number that your accounts use for recovery and one-time codes. A victim who has done everything right on the DNS and router side can still be compromised if their carrier can be socially engineered into porting their number to an attacker's device. Efani's SAFE plan is built specifically to prevent that, and you can check your own number with a free SIM-swap vulnerability scan to see how exposed it currently is.
Final Thoughts
Pharming is harder to spot than ordinary phishing because it removes the one thing most of us have been trained to watch for: the suspicious link. Protecting against it means securing the infrastructure between you and the websites you trust, your router, your DNS, your device, rather than just your inbox. Combined with HTTPS checks, two-factor authentication, and up-to-date anti-malware protection, these steps close off the paths pharming relies on.
FAQ
Q: What is pharming in cybersecurity?
A: Pharming is an attack that redirects you to a fake website by manipulating DNS records or infecting your device's hosts file, rather than by tricking you into clicking a malicious link.
Q: How is pharming different from phishing?
A: Phishing requires a lure, like a deceptive email or text, to get you to click something. Pharming redirects you automatically once the DNS or device-level manipulation is in place, with no click or lure needed at the moment of redirection.
Q: Can pharming happen even if I type the website address myself?
A: Yes. Because pharming manipulates the translation of a domain name to an IP address (or your device's hosts file), typing the correct address or using a bookmark does not protect you if the manipulation has already occurred.
Q: How do I know if my router has been compromised for pharming?
A: Warning signs include unexpected redirects, devices on your network reaching unfamiliar versions of familiar sites, or DNS settings in your router's admin panel that you did not configure. Checking and resetting your router's DNS settings and admin password is a reasonable first response.
Q: Does HTTPS protect against pharming?
A: It helps. A pharming site impersonating a well-known service will often fail to present a valid HTTPS certificate for that domain, which is a strong warning sign, but it is not a complete guarantee, so pair HTTPS checks with two-factor authentication and router/DNS hygiene.
Q: Are the pharming examples people cite online always accurate?
A: Not always. Several widely repeated pharming anecdotes online omit sources entirely. The three incidents cited above (2007, 2015, 2019) are each tied to a specific, named, dated source rather than repeated secondhand.