What Is Data Exfiltration, and How Do You Protect Against It?


Introduction
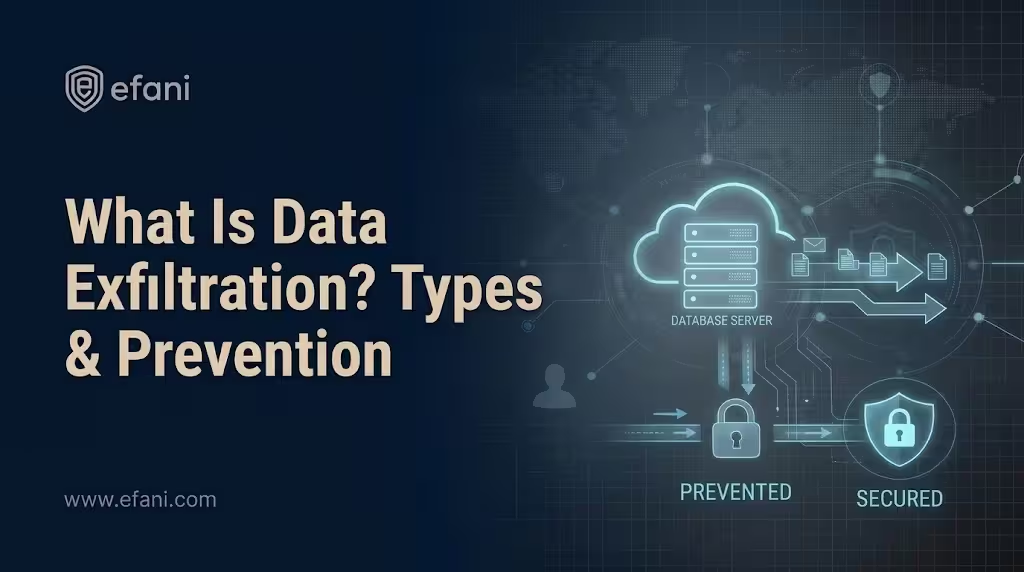
Data exfiltration is the unauthorized transfer of data out of a computer system, network, or organization. It is the step in a breach where "an attacker got in" becomes "an attacker got something out," and it is the step that turns an intrusion into financial loss, identity theft, regulatory exposure, and reputational damage.
What Is Data Exfiltration?
Also called data extrusion, data exfiltration is the theft of confidential or sensitive data, carried out by external hackers, malicious actors who have gained access, or insiders such as disgruntled employees. The data itself can be anything of value: customer records, financial files, source code, emails, or intellectual property. It is usually stolen through malware that has already gained a foothold on a system, through direct, unauthorized network access, or in some cases through old-fashioned physical theft of a device.
Is your cellphone vulnerable to SIM Swap? Get a FREE scan now!
Please ensure your number is in the correct format.
Valid for US numbers only!
How Attackers Exfiltrate Data
Exfiltration techniques are generally grouped into two categories:
- Passive exfiltration – the attacker does not directly, interactively access the system. Instead, they get in through indirect means, like a phishing email or a malware infection, and the stolen data makes its way out through that initial foothold.
- Active exfiltration – a more direct approach where the attacker actively navigates the compromised system, hunting for specific valuable data and moving it out deliberately, often using a live network connection they control.
Common real-world scenarios include:
- Phishing emails carrying malicious links or attachments that install malware capable of harvesting and exporting data
- Malware that tracks activity, steals credentials, and exfiltrates files once installed
- Direct network access gained by exploiting an unpatched vulnerability or stolen credentials
- Insider threats, where someone with legitimate access deliberately removes data they are not authorized to take
Why Data Exfiltration Has Become More Central to Ransomware
The threat landscape around exfiltration has shifted meaningfully in recent years. Ransomware groups increasingly steal data before encrypting anything, so that even an organization with solid backups still faces pressure: pay up, or the stolen data gets published or sold. This "double extortion" model (and in some cases, extortion without any encryption at all, just the threat of leaking what was stolen) has made exfiltration itself, not just encryption, the leverage point attackers rely on.
BlackFog's Q2 2026 ransomware report, covering April through June 2026, found that 97% of publicly disclosed ransomware incidents that quarter involved data exfiltration, the highest rate the firm says it has recorded. The same report tracked a separate, and arguably more alarming, trend: ransomware attacks that victims never disclose at all, identified instead through dark-web leak-site monitoring, rose 40% year-over-year (2,027 such attacks in Q2 2026 versus 1,446 in Q2 2025), with an average of 508 GB of data stolen per undisclosed incident. Treat this as one vendor's dataset and methodology rather than a universal constant, since figures vary by how each research firm tracks and defines an incident, but the direction is consistent across the industry: exfiltration is now the default, not the exception.
How to Prevent Data Exfiltration
A layered approach works best, since no single control catches everything:
- Use strong, unique passwords on all accounts with system access, and retire shared or default credentials.
- Monitor user activity for behavior that deviates from the norm, such as a user suddenly accessing files far outside their usual scope.
- Implement multi-factor authentication on every account that can reach sensitive systems.
- Encrypt sensitive data, both at rest and in transit, so stolen data is far less useful even if it does leave the network.
- Monitor outbound network traffic, not just inbound, since exfiltration is fundamentally a data-leaving-the-network event.
- Keep software patched and current to close the vulnerabilities attackers rely on for initial access.
- Train employees on phishing recognition and safe data-handling practices.
- Deploy data loss prevention (DLP) tooling to flag or block unauthorized transfers of sensitive data.
SIM Swap Protection
Get our SAFE plan for guaranteed SIM swap protection.
Adopting a Zero-Trust Mindset
A zero-trust security model, built on "never trust, always verify," has become one of the more durable frameworks for exfiltration prevention because it assumes a malicious actor could already be inside the network, rather than trusting anyone by default once they are past the perimeter. In practice that means strong identity management, granular access control, encryption, and continuous logging of who accessed what, when. It is a meaningful shift from older perimeter-only thinking, but it is also an ongoing program, not a single tool you install once.
Detecting an Exfiltration Attempt
Detection is harder than prevention, but a few practices make a real difference:
- Monitor access logs for unauthorized access to sensitive data
- Watch for unusual outbound network traffic patterns, especially large transfers to unfamiliar destinations
- Keep intrusion detection systems tuned and current
- Scan regularly for malware that may already be resident on a system
- Review system performance for anomalies that could indicate background data movement
Monthly
Yearly
Having an Incident Response Plan Ready
When exfiltration does happen, response speed matters. A workable incident response plan defines the scope of the breach quickly (what data, which systems, who is affected), contains the immediate threat (isolating affected systems, rotating credentials), investigates the root cause, and documents what happened and what changes follow. Treating this plan as a living document, reviewed and rehearsed periodically rather than written once and filed away, is what actually makes it useful when an incident occurs.
The Exfiltration Risk Most Prevention Plans Miss
Most data exfiltration prevention programs focus entirely on the corporate network: firewalls, DLP tooling, access controls. Very few extend that same scrutiny to the mobile number tied to the executives and employees who hold the keys to those systems. A SIM swap gives an attacker control of a victim's phone number, and with it, the ability to intercept SMS-based one-time codes and password reset links used to reach the very accounts a DLP program is trying to protect. It is a gap worth closing directly. Efani's SAFE plan is built to prevent SIM swapping, and a free SIM-swap vulnerability scan takes only a couple of minutes to check your own number's exposure.
Final Thoughts
Data exfiltration is a growing threat precisely because it is the payoff step for so many other attacks, from phishing to ransomware to insider misuse. No single control stops it reliably on its own. A layered defense of strong authentication, encryption, outbound traffic monitoring, employee training, and a zero-trust mindset, backed by a tested incident response plan, gives organizations the best realistic chance of catching an exfiltration attempt before the data is gone for good.
FAQ
Q: What is the difference between data exfiltration and a data breach?
A: A data breach is the broader event of unauthorized access to a system. Data exfiltration specifically refers to the step where data is actually transferred out of that system; a breach can occur without exfiltration if the attacker never removes any data.
Q: Is data exfiltration always carried out by outside hackers?
A: No. A meaningful share of exfiltration incidents involve insiders, such as employees or contractors who misuse legitimate access to remove data they are not authorized to take.
Q: Can data exfiltration happen without triggering an alert?
A: Yes, especially with slow, low-volume transfers designed to blend in with normal traffic. This is exactly why outbound traffic monitoring and behavioral analysis matter as much as perimeter defenses.
Q: Why has data exfiltration become central to ransomware attacks?
A: Many ransomware groups now steal data before encrypting systems, so they can threaten to leak or sell it even if the victim has backups and refuses to pay for a decryption key. BlackFog's Q2 2026 data put exfiltration in 97% of publicly disclosed ransomware incidents, the highest rate it has recorded.
Q: Does encrypting my data stop exfiltration?
A: Encryption doesn't stop data from leaving the network, but it significantly reduces its value to an attacker if it does, since properly encrypted data is unusable without the decryption key.